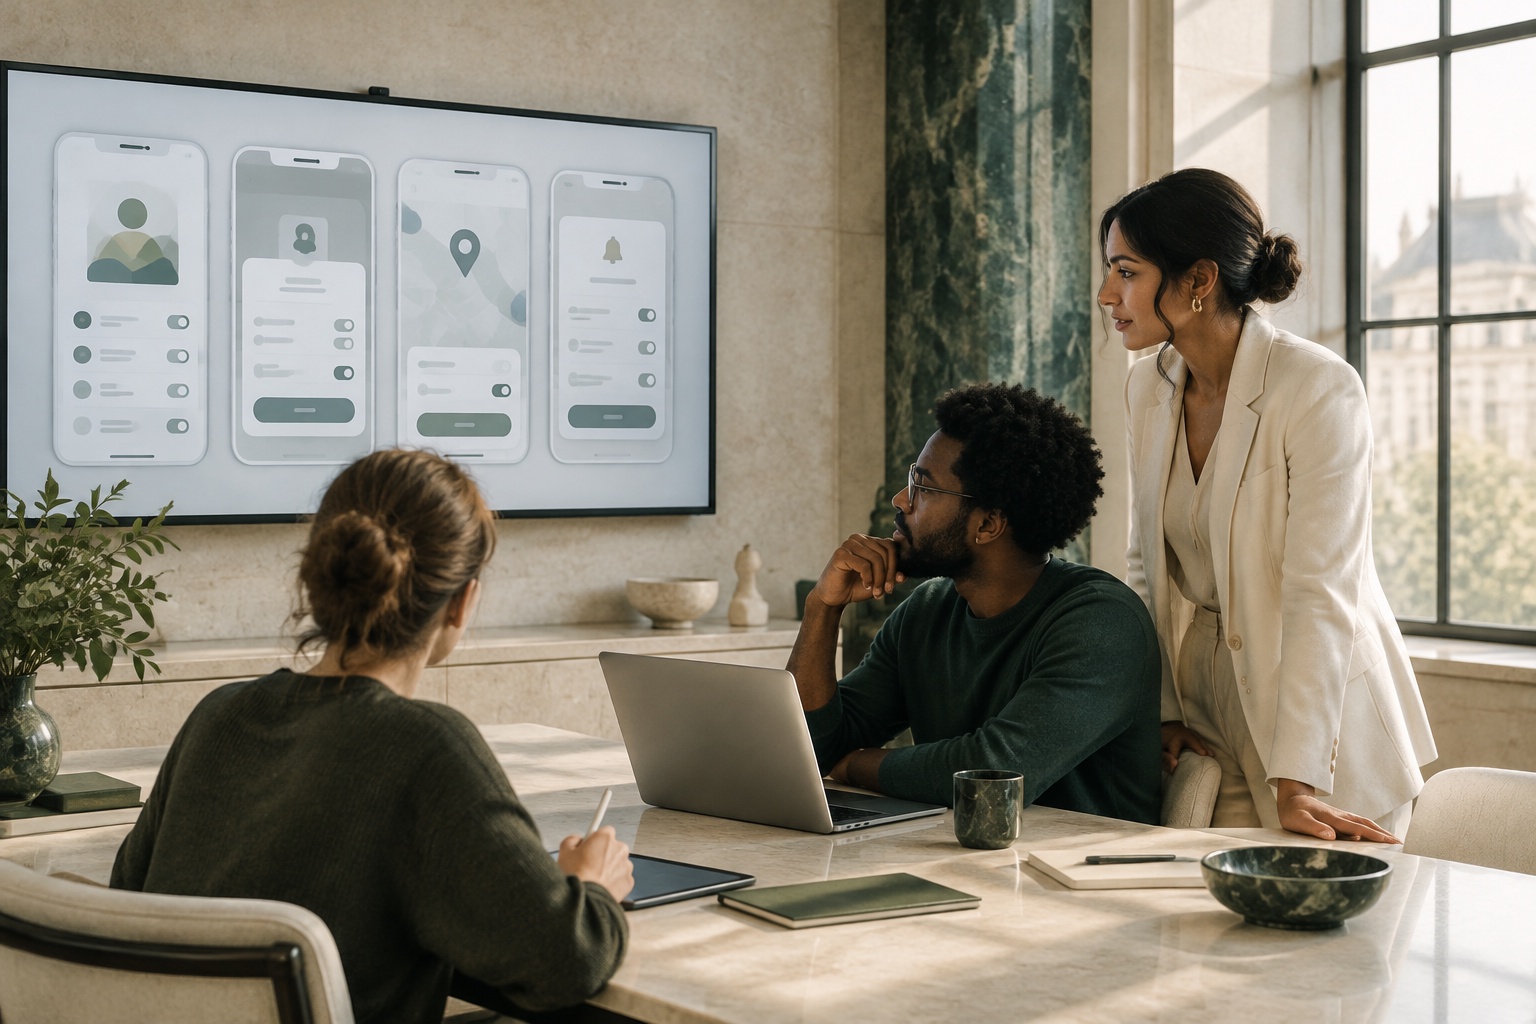
The best privacy notices today are not documents. They are moments of clarity built into the product, at the exact point a user needs to decide, and they stay accurate as the product evolves. This guide is for the people who build that product: product managers, designers and engineers.
Why the privacy notice outgrew the footer
For two decades, the privacy notice was a long legal page linked from the footer, written to satisfy a regulator and read by almost no one. That model is breaking down for three reasons.
Regulators now judge the moment, not the page. Privacy laws such as Quebec's Law 25 and PIPEDA, and international standards such as the GDPR, expect information to be given at or before the point of collection, in terms a user can understand. Canada's privacy commissioner has made the same point about AI: information about a system must be understandable at the point where it affects an individual's decision.
AI changed what users need to know. When a product can summarize, recommend, generate or decide, users want to know whether they are talking to a person or a machine, what the system can see, and whether their content trains the model. New rules such as Article 50 of the EU AI Act turn those expectations into obligations.
Trust became a product metric. Users abandon flows they do not understand and revoke permissions they feel were taken. Clear transparency at the right moment increases opt-in rates for features that genuinely need data, because users understand why.
Seven best practices for modern privacy notices
- Start from the data, not a template. A notice is only as good as the data map behind it. Talk to the people who built the product: what is collected, from where, for which purpose, shared with whom, stored where and kept for how long.
- Layer it. Give users a short summary first, plain-language detail second and the complete legal record third. Each layer should be useful on its own.
- Go just-in-time. Place short notices where data is collected: the permission prompt, the form field, the camera button, the location toggle. One or two sentences, with a link to more.
- Write for a person in a hurry. Short sentences, active voice, concrete examples. "We use your location to show nearby stores" beats "location data may be processed for service-related purposes."
- Be specific about purposes. Vague catch-alls such as "to improve our services" invite complaints. Name the purpose, and say plainly when data is used for advertising, profiling or AI training.
- Make rights easy to use. Tell users exactly how to access, correct, delete or withdraw consent, and make the path as short as the one used to sign up.
- Design it accessibly. Readable contrast, screen-reader friendly structure, mobile-first layout and the languages your users actually use.
AI transparency: the patterns that build trust
Since generative AI entered everyday products, a set of transparency patterns has emerged in the products people actually choose to use. None of them is a paragraph buried in a policy. Each one sits in the interface.
AI interaction label
- What users see
- A clear badge or line telling users they are interacting with an AI system, not a person
- Why it works
- Removes the deception risk and sets expectations before the first message
AI-generated content label
- What users see
- "AI-generated" or "edited with AI" on text, images, audio or video
- Why it works
- Lets users judge reliability and supports content-marking rules
Scope of access
- What users see
- A short note on what the assistant can read: this document, this workspace, your email
- Why it works
- Answers the first question users ask about any AI feature
Training choice
- What users see
- A plain statement of whether user content trains the model, with a visible toggle where a choice exists
- Why it works
- Addresses the single biggest trust concern with AI tools
"Why am I seeing this"
- What users see
- A tap-to-explain link on recommendations, rankings or flags
- Why it works
- Makes automated outputs understandable without a lecture
Decision explanation and human review
- What users see
- For automated decisions with real consequences, the main factors used and a way to reach a person
- Why it works
- Meets automated decision rules and keeps users in control
Public AI page
- What users see
- A plain-language page listing AI features, models or vendors used, data used and limits
- Why it works
- Gives journalists, buyers and regulators one honest reference point
Feedback and correction
- What users see
- A way to flag a wrong or harmful output
- Why it works
- Shows the system is supervised and improving
| Pattern | What users see | Why it works |
|---|---|---|
| AI interaction label | A clear badge or line telling users they are interacting with an AI system, not a person | Removes the deception risk and sets expectations before the first message |
| AI-generated content label | "AI-generated" or "edited with AI" on text, images, audio or video | Lets users judge reliability and supports content-marking rules |
| Scope of access | A short note on what the assistant can read: this document, this workspace, your email | Answers the first question users ask about any AI feature |
| Training choice | A plain statement of whether user content trains the model, with a visible toggle where a choice exists | Addresses the single biggest trust concern with AI tools |
| "Why am I seeing this" | A tap-to-explain link on recommendations, rankings or flags | Makes automated outputs understandable without a lecture |
| Decision explanation and human review | For automated decisions with real consequences, the main factors used and a way to reach a person | Meets automated decision rules and keeps users in control |
| Public AI page | A plain-language page listing AI features, models or vendors used, data used and limits | Gives journalists, buyers and regulators one honest reference point |
| Feedback and correction | A way to flag a wrong or harmful output | Shows the system is supervised and improving |
What the law expects. Quebec's Law 25 requires organizations to inform people when a decision about them is based exclusively on automated processing. International standards point the same way: the EU AI Act requires that people be told when they interact with an AI system and that certain AI-generated content be disclosed. Same direction everywhere: tell people, at the right moment, in words they understand.
The practical takeaway. Treat every AI feature as a disclosure moment. Before it ships, decide what the user sees, where, and what they can do about it.
Choices inside the product, without dark patterns
A notice is only as honest as the interface around it. Dark patterns steer users toward choices against their own interest, and Quebec's privacy regulator treats consent obtained this way as invalid.
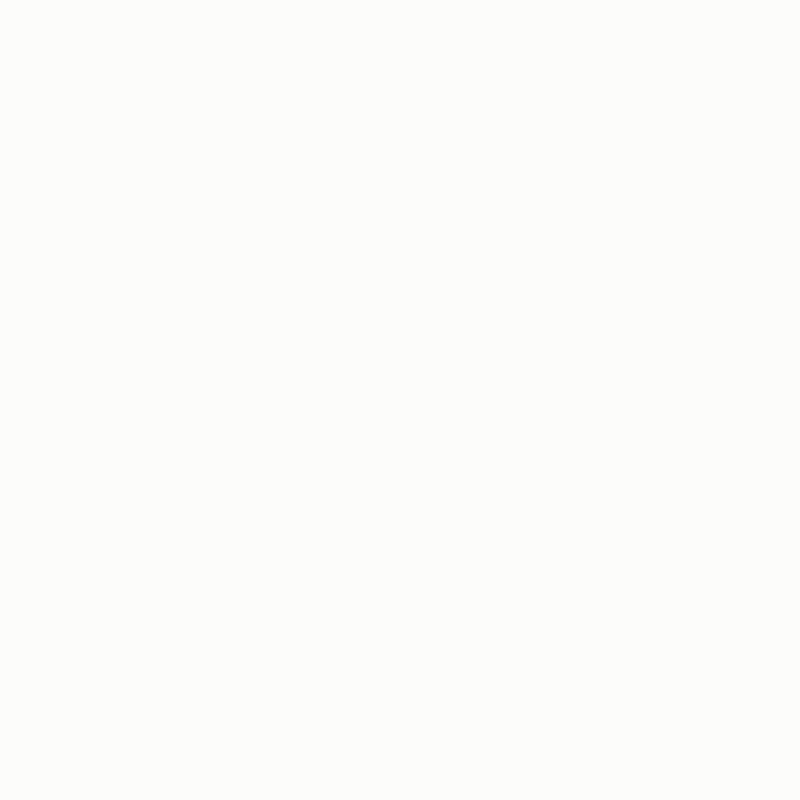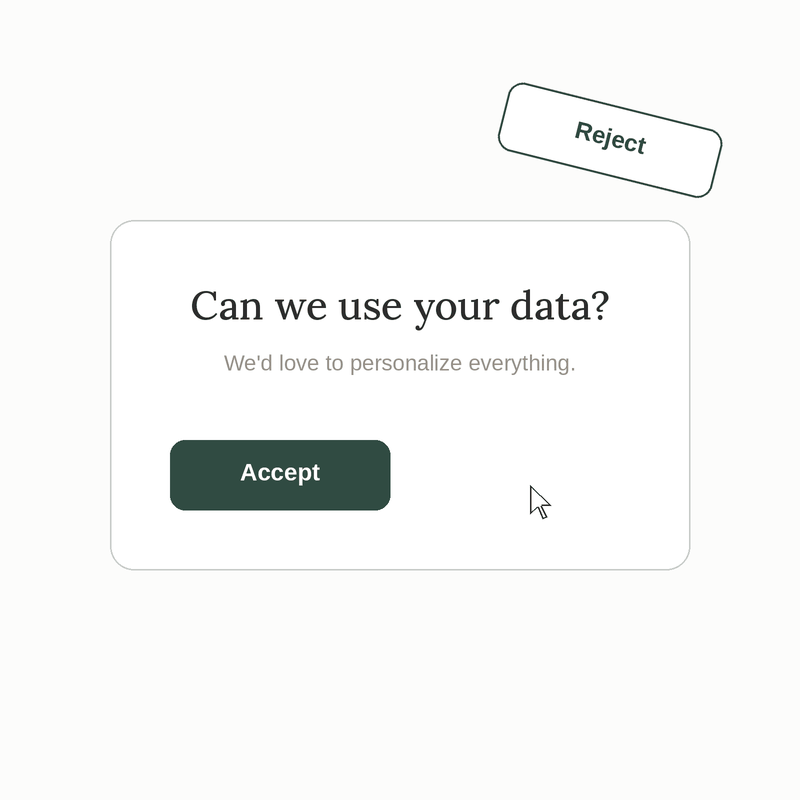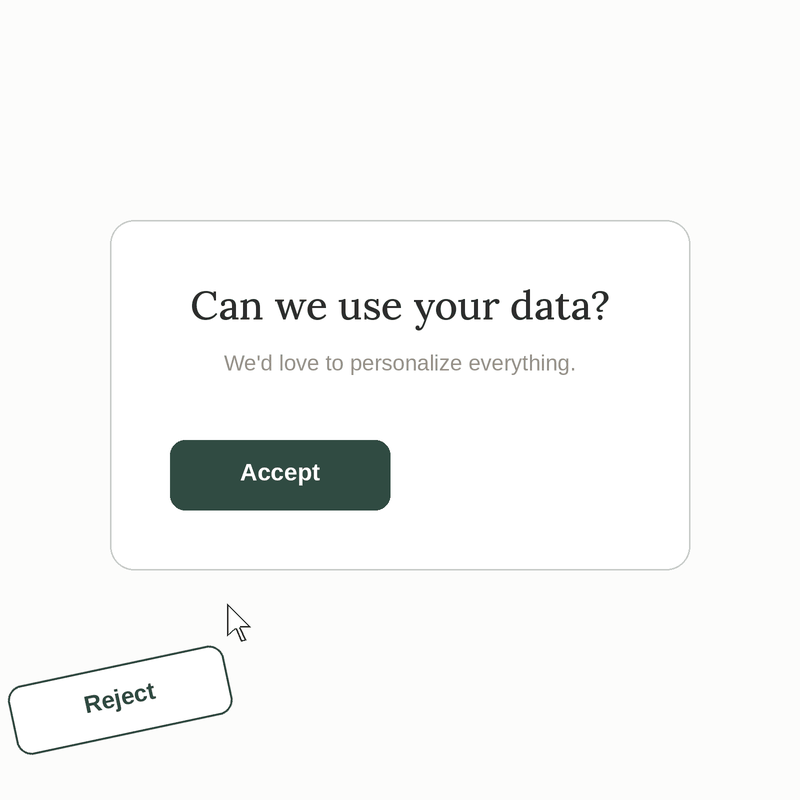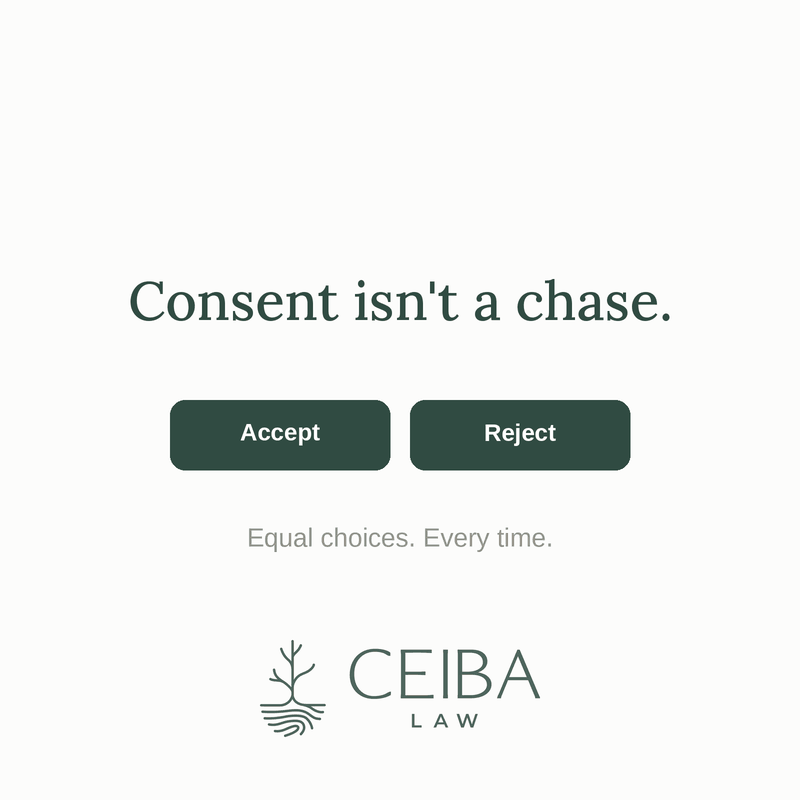
Consent isn't a chase: when refusing is harder than accepting, the choice is not free.
- Equal weight. "Accept" and "Reject" look the same and sit side by side.
- Same effort. Refusing takes no more steps than accepting.
- Optional means off. Nothing optional is pre-checked.
- Easy to undo. A choice can be changed later as easily as it was given.
Examples for information only; what is appropriate depends on your product, jurisdiction and context.
Questions about consent or dark patterns in your product?Contact us
Cookie banners, email tracking and marketing consent raise their own questions, which deserve a separate look with your marketing team.
A privacy notice is not a paper: keeping it alive
The most common privacy notice failure is not bad drafting. It is drift. The notice was right at launch, then the product added a vendor, an AI model, a new data field or a new market, and nobody updated the words. Modern teams treat the notice like code: versioned, reviewed and shipped with the feature.
- Build privacy into the release process. Add one question to every feature ticket: does this change what we collect, why, or who we share it with? If yes, the disclosure ships with the feature.
- Set up a notification center. An in-product space where users see material changes in plain words, review consents and adjust settings. Far more effective than an email nobody opens.
- Notify the right users. A change to how payment data is handled matters to paying customers, not to every visitor. Decide who must be told, who must re-consent, and who simply sees a dated changelog.
- Keep a version history. Store every notice and consent version with dates, so you can prove what a given user saw and agreed to at any time.
- Review on a schedule and on triggers. An annual review, plus an immediate one when you add AI features, enter a new jurisdiction, change a key vendor or when the law changes.
Checklist for product teams
Your product team should have a consent check available to them that looks like the one below. Each legal framework and situation is different, so these are non-exhaustive points to consider, not a complete compliance test.
- Our notice is built from a current data map, reviewed with product and engineering
- The notice is layered: summary, detail, full record
- Every data collection point in the product has a just-in-time notice
- The privacy notice is available at the point of collection, so consent is informed even when it is implicit
- Consent is specific, informed and time-bound, and the collection it covers is reasonable and proportionate to the purpose
- Individuals are told their rights, such as access, correction and withdrawal of consent, and how to exercise them
- Express consent is obtained when the law requires it, for example for sensitive information or secondary uses
- Consent is not bundled: each purpose that needs consent is presented and accepted separately, not hidden in terms of use
- Permissions are requested in context, when the user reaches the feature that needs them
- Every AI feature tells users they are dealing with AI, what it can access and whether their content trains it
- AI-generated content is labelled where users will see it
- Automated decisions with real consequences come with an explanation and a path to a human
- Optional data uses are easy to switch on; in most cases, keeping them off by default is recommended, depending on the jurisdiction
- Users can reverse any choice as easily as they made it, from one privacy settings screen
- No dark patterns: accept and refuse options have the same size, colour and placement, refusing takes no more steps than accepting, nothing is pre-checked, and no wording pressures or guilts the user
- A notification center explains material changes
- Every notice and consent version is dated and stored
- Consent withdrawals are documented, dated and applied to every system that uses the data
- Privacy review is part of our release process
How Ceiba can help
A privacy notice is the visible part of the work. We advise and support product teams on everything behind it: mapping how personal information really flows, scanning and verifying what your products collect, building consent into each step, and implementing the processes that keep your notices accurate as you ship.
Learn more about our Privacy Notices service or contact us.
This article is general information, not legal advice.